Loading video…
All breakouts
5.6Talking HeadHow-To hookEducation
Hook
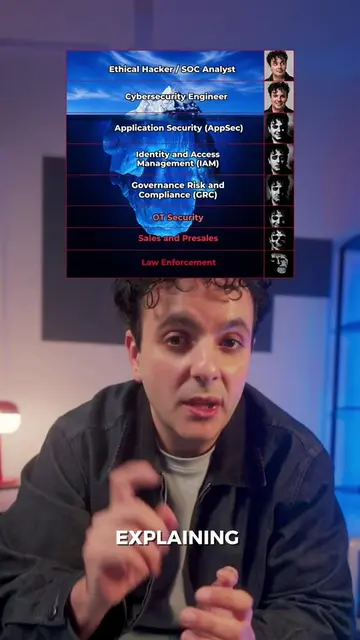
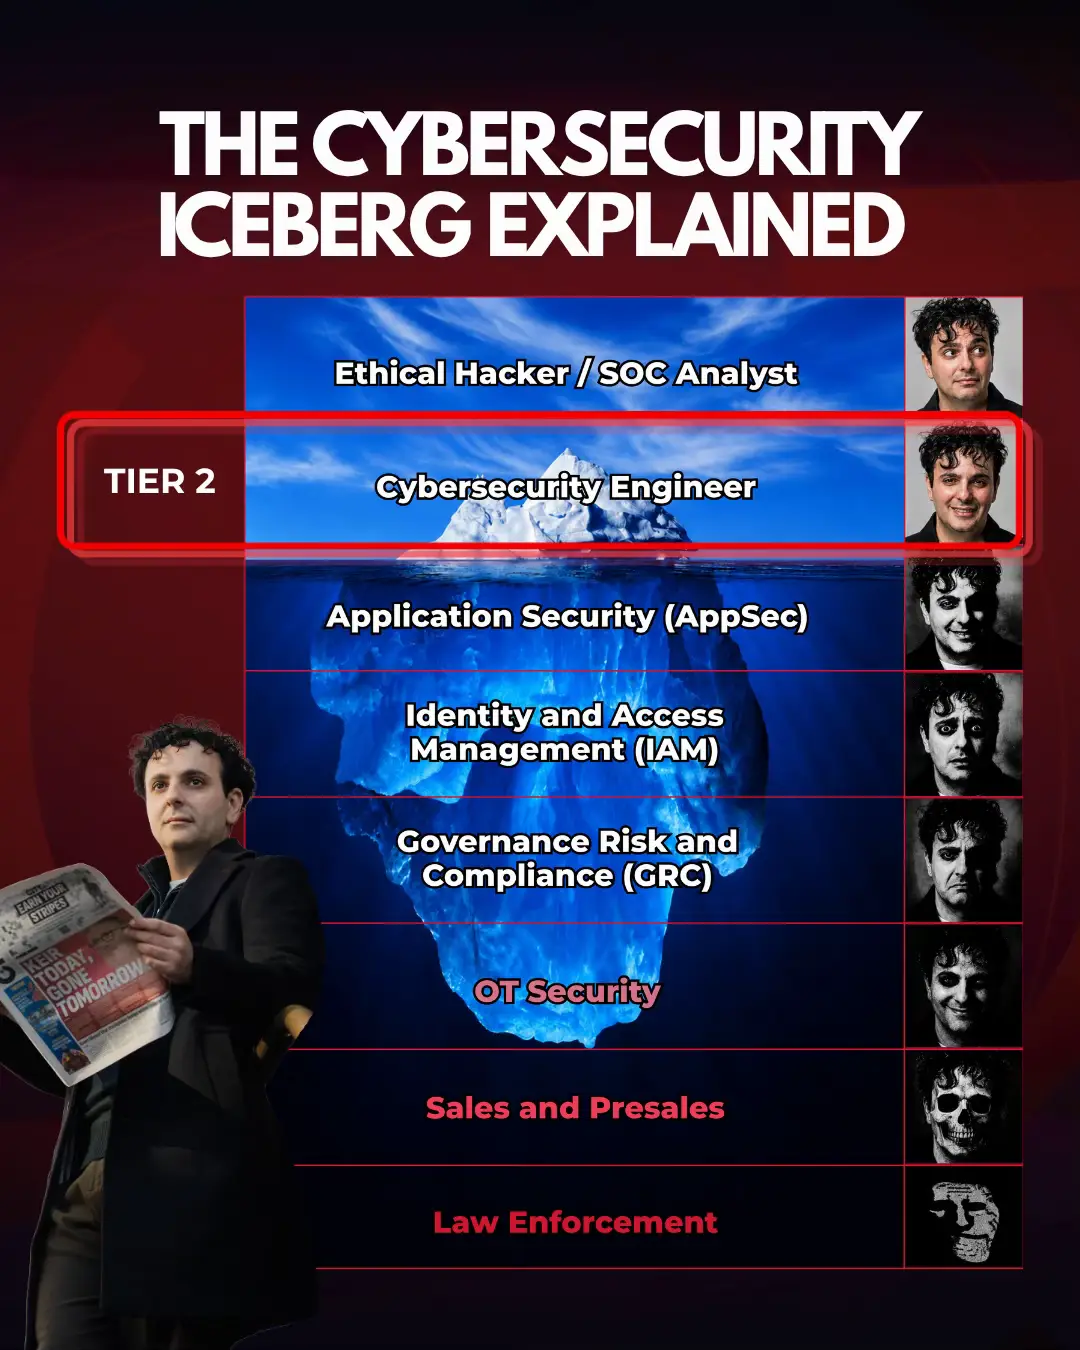
Explaining the cybersecurity jobs iceberg
@unixguy_cybersecurity
115.9K followers · usually 3.7K views a post
Views
20.6K
Likes
1.1K
Comments
18
Shares
51
Why it worked
The video uses a popular 'iceberg' format to break down complex information about cybersecurity careers, making it easily digestible and engaging. It also highlights a niche but growing field (GRC) that offers good career prospects, appealing to viewers interested in career advancement.
Summary
The video explains the cybersecurity job market using an iceberg analogy, detailing roles from most common to more niche. It highlights Governance, Risk, and Compliance (GRC) as a crucial, often misunderstood, and potentially lucrative area within cybersecurity with good work-life balance and career progression opportunities.
Structure
- 1Introduction to cybersecurity job iceberg
- 2Explanation of GRC's role
- 3Job market for GRC professionals
- 4Work-life balance and career path in GRC
- 5Misinformation and challenges in GRC
Product placement
GRC Security: APPEARS - A category of cybersecurity jobs. Removing it would not change what happens in the video.
GRC: ACTS - The speaker discusses the function and importance of GRC in cybersecurity roles. Removing it would change what happens in the video.
GRCMastery.com: ACTS - The speaker mentions this website as a resource for learning about GRC. Removing it would change what happens in the video.
Cohere Technologies: ACTS - The company is presented as a potential employer, and the video discusses a job opening within the company. Removing it would change what happens in the video.
Chief Information Security Officer (CISO): ACTS - This is a job title discussed in the context of career progression within cybersecurity. Removing it would change what happens in the video.
NVIDIA: APPEARS - Mentioned as a company that builds AI systems. Removing it would not change what happens in the video.
AI: ACTS - Discussed as a technology that Cohere builds and deploys, and that requires security. Removing it would change what happens in the video.
Original caption
Tier 5 : GRC As we go deeper into the iceberg, you’ll find less people who understand the job. GRC is widely misunderstood, with a lot of misinformation about it online :) it’s a great area to get into in cybersecurity! #cybersecuritycareers #iceberg #grc
More from @unixguy_cybersecurity
More breakout videos from this creator.